Skip to content
Secure Open Solutions

Choose your view. Explore at your own pace.

Start with plain-language guidance for decision makers: what each service helps you achieve, what to expect, and how to take the next step.
Expand the architecture, security controls, implementation scope, and detailed reference guidance on this page. Your planner choices and inquiry stay in place.

GOVERNMENT SYSTEM APPROVAL SUPPORT

Move your system toward government approval.

Turn a complex approval effort into a defined cybersecurity work plan, with clear responsibilities, documents and milestones for your team and partners.

What you can expect

  • A clear work package and responsibility plan
  • A better-organized set of approval materials
  • Support for reviews and continuing follow-up

What to bring to the first discussion

  • Who owns the system and makes the approval decision
  • The milestone or proposal deadline
  • The work your team and partners expect SOS to cover

The responsible government authority makes the approval decision. Support work or an assessment finding is not that approval.

Show technical scope and implementation detail

RMF / ATO and teaming support · Scope is confirmed against your requirements.

Authorization scope

  • Identify the system owner, authorizing organization and RMF / ATO milestone.
  • Define system boundaries, interfaces, inherited controls and expected artifacts.

Delivery and teaming

  • Agree on responsibility allocation, workshare and assessment support.
  • Plan SSP / POA&M work, evidence readiness and continuing monitoring within the agreed engagement.
  • Account for OT and specialized-asset constraints where applicable.
Explore the detailed service guidance

Home / Details

RMF / ATO

Connect mission requirements and the system boundary to the selected control baseline, authorization evidence, and ongoing monitoring.

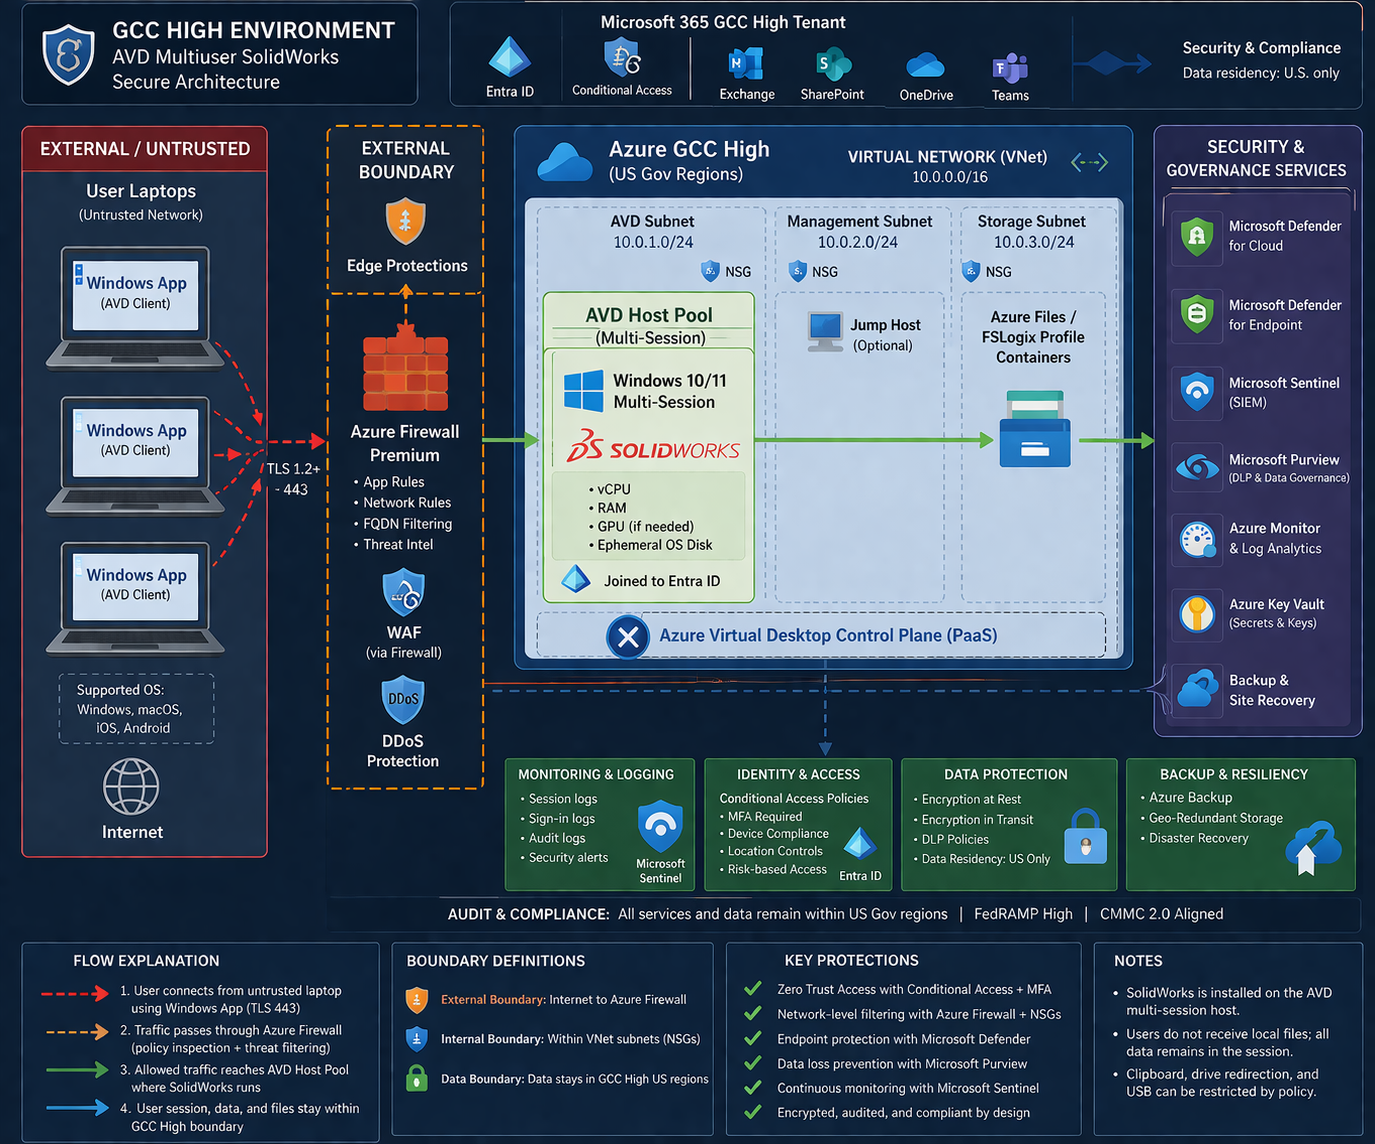
RMF / ATO reference diagram
Reference illustration. Select the image to send an inquiry or schedule an appointment. Service configuration and control responsibilities are validated for the actual deployment.

Authorization workstream

  • Define the system and its dependencies, categorization inputs, and authorization strategy.
  • Allocate internal, inherited, and shared responsibilities; tailor the baseline with the authorizing organization.
  • Prepare implementation narratives, assessment evidence, findings and POA&M records.

Deliverables

  • System boundary and control-responsibility mapping.
  • SSP, assessment preparation and authorization-package support.
  • eMASS workstream coordination and continuous-monitoring plan.

What SOS needs from the customer

A system owner, authorization stakeholders, existing package artifacts, provider inheritance evidence, and access to the personnel responsible for implementation.