Skip to content
Secure Open Solutions

Choose your view.
Explore at your own pace.

Start with plain-language guidance for decision makers: what each service helps you achieve, what to expect, and how to take the next step.
Expand the architecture, security controls, implementation scope, and detailed reference guidance on this page. Your planner choices and inquiry stay in place.

PROTECTED WORK ENVIRONMENT

Give sensitive work a protected place.

Create a defined place for the information, applications and people that need stronger protection. We help match the design to how your team actually works.

What you can expect

  • A clear design for access and information movement
  • A practical implementation and operating plan
  • A handover that makes responsibilities clear

What to bring to the first discussion

  • How people work with the information today
  • The applications, devices and locations involved
  • Customer requirements and limits on sharing or downloading

The environment must fit your workflow and requirements. Buying or deploying a system alone does not establish compliance.

Show technical scope and implementation detail

Secure enclave implementation · Scope is confirmed against your requirements.

Architecture and boundary

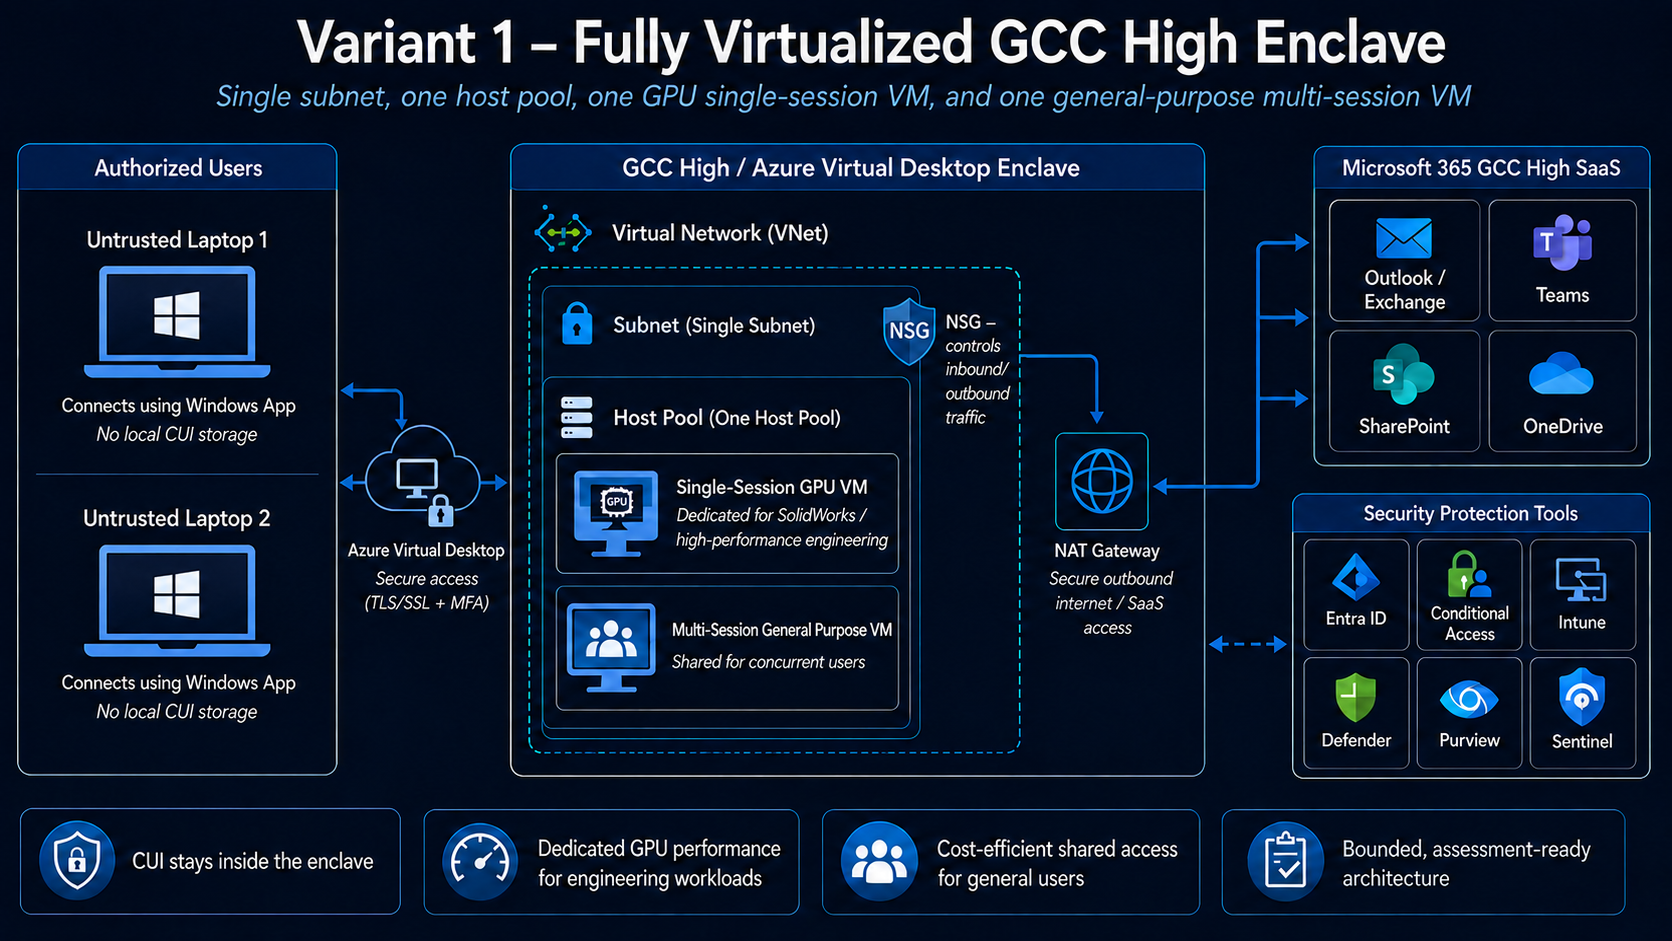
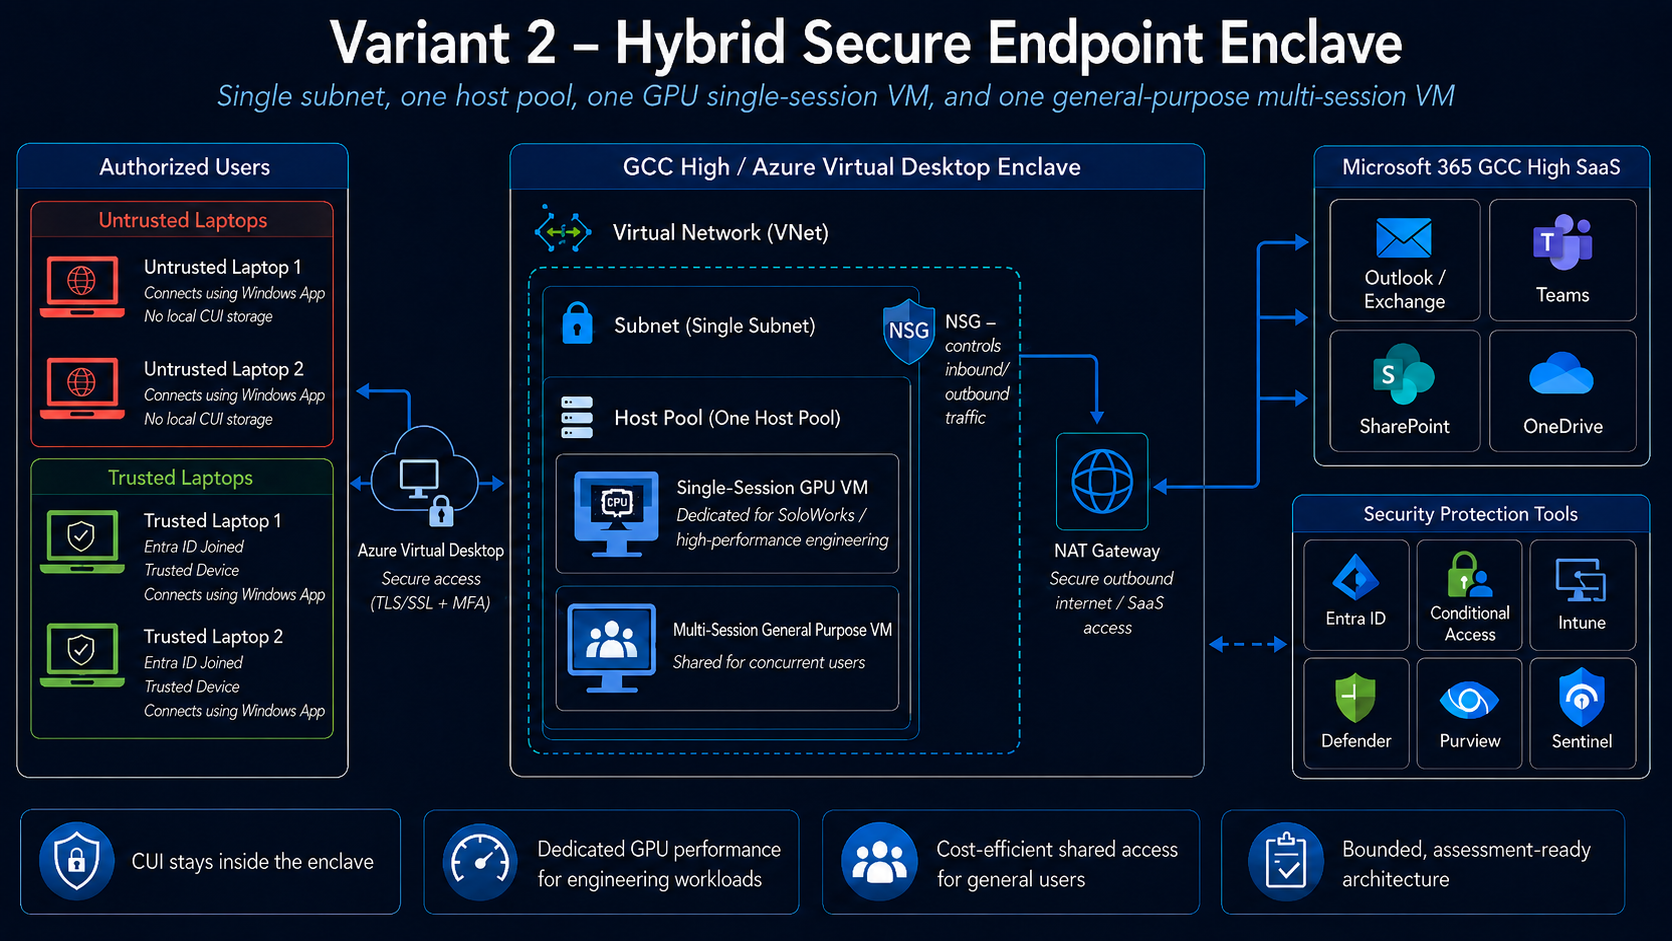
  • Consider GCC High, Azure Government, AVD and hybrid patterns against the actual workflow.
  • Define identity, session access, network segmentation and permitted data flows.

Operation and evidence

  • Agree on device restrictions, encryption, logging, backup and administrative responsibilities.
  • Document the boundary and safeguard configuration for the agreed scope.
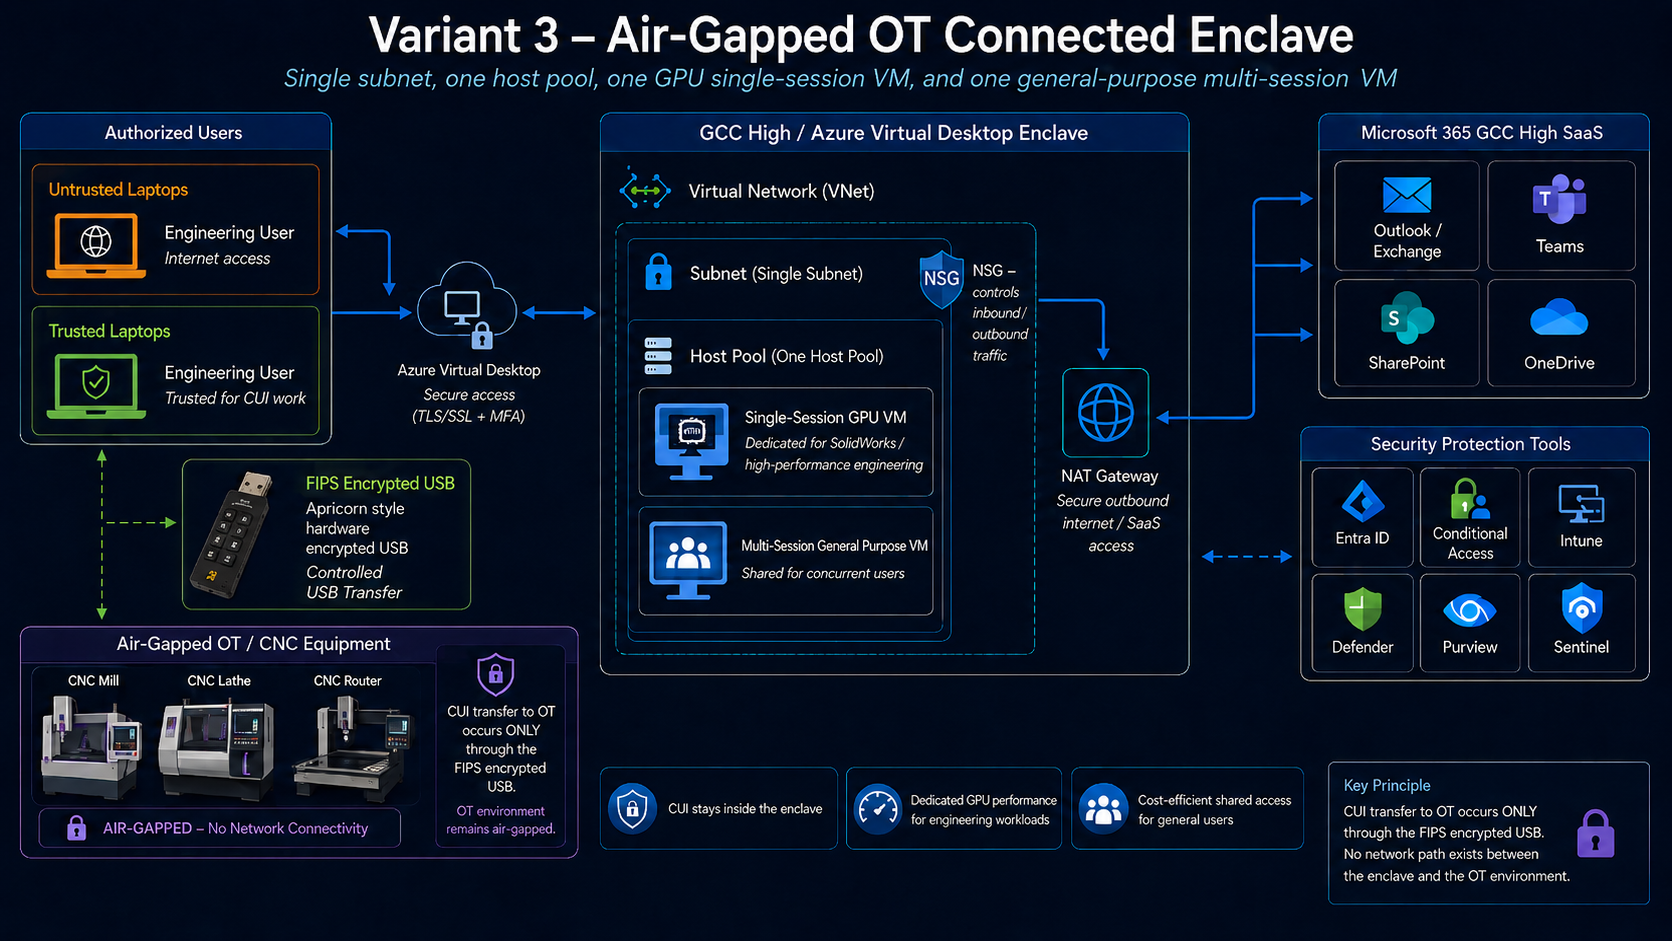
  • Confirm specialized-asset and external-provider interfaces rather than assuming they fit a standard cloud pattern.
Explore the detailed service guidance

GCC High & Azure Government enclaves

The right boundary. A repeatable deployment.

Build a focused CUI environment with GCC High, Azure Government and AVD isolation. Infrastructure as code supports a turnkey, scalable and repeatable delivery model.

What SOS helps you accomplish.

01

Choose the architecture

Align desktop access, cloud workloads and specialized equipment to the way your people handle CUI.
02

Deploy the foundation

Use versioned IaC templates and reviewed parameters for network segmentation, cloud resources and AVD capacity.

03

Protect & operate

Configure identity, endpoints, data protection and monitoring. Validate controls, retain evidence and plan approved scaling.

Choose the boundary that fits.

Compare three workflows, then validate the architecture and control responsibilities.