
SECURE OPEN SOLUTIONS
CMMC RPO / C3PAO
Prepare your organization for CMMC, or plan an independent assessment. Choose the path that fits your next milestone.
Explore the details
Identity and Access
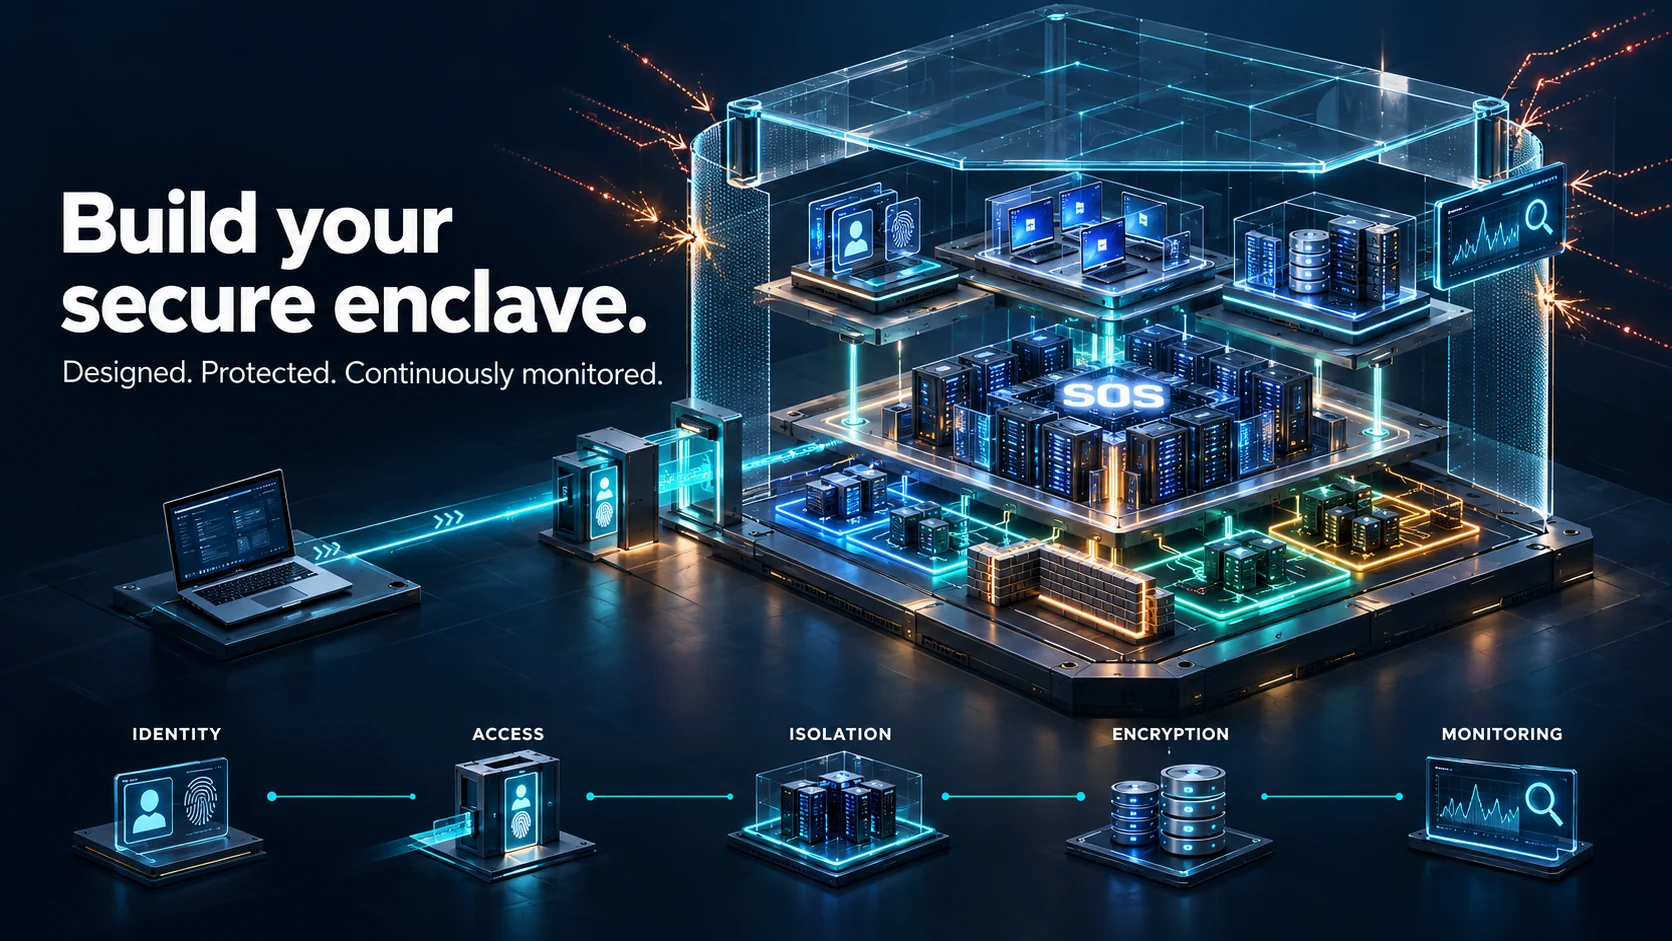
Identity and access work defines who may use protected information, which devices they may use, and what they can do after signing in. It connects business responsibilities to account approvals, authentication, permissions and the removal of access when circumstances change.
What this includes
- Map employees, administrators, service accounts and external users to their responsibilities
- Review access approvals, authentication, privileged access and separation of duties
- Establish recurring reviews and a dependable process for role changes and departures
A reviewable access model links each permission to an owner, a business reason and evidence of approval. That model should be reflected in actual system settings, rather than existing only in a policy.
Explore details →Protected Workspace
A protected workspace is a defined operating environment for sensitive work. Its design starts with the information and business workflow, then identifies the users, endpoints, applications, cloud services and data transfers that belong inside the scope.
What this includes
- Trace how information enters, is processed, is stored and leaves the workspace
- Identify endpoints, shared services, supplier dependencies and customer responsibilities
- Translate the approved boundary into access, network, data-handling and operating procedures
A clear boundary helps the organization operate its safeguards and explain them consistently. It also identifies work that remains with the customer, including user behavior, endpoint responsibilities and the handling of approved transfers.
Explore details →Monitoring and Evidence
Monitoring and evidence management keep the documented security story connected to daily operations. Useful evidence shows that safeguards are implemented, reviewed and maintained; it should identify what happened, who was responsible and which system or requirement the record supports.
What this includes
- Assign owners and review dates to evidence and recurring security activities
- Connect configuration changes, findings and remediation to the relevant system scope
- Check whether procedures, SSP narratives and actual implementation remain consistent
The result is a maintained evidence set and a clear action trail. Teams can find current records, distinguish a completed activity from a planned one, and understand what must be updated after a system or responsibility changes.
Explore details →Scope and Deliverables
A useful CMMC readiness and independent assessment engagement begins with a defined boundary, an agreed outcome and a clear division of responsibilities. Scope makes the work understandable before estimates and schedules are finalized, and deliverables describe what the customer will be able to review or use.
What this includes
- Confirm the systems, business needs, applicable requirements and delivery constraints
- Agree roles, inputs, exclusions, acceptance criteria and review milestones
- Identify the records, procedures and implementation work needed to support the outcome
The result is a practical statement of work with reviewable outputs and accountable owners. Assumptions and dependencies remain visible so changes can be assessed before they affect cost or schedule.
Explore details →Readiness consulting and independent assessments are separate engagements. Assessment eligibility, conflicts and impartiality are reviewed before acceptance.