Skip to content
Secure Open Solutions

Home / Details

Variant 1 — Fully virtualized enclave

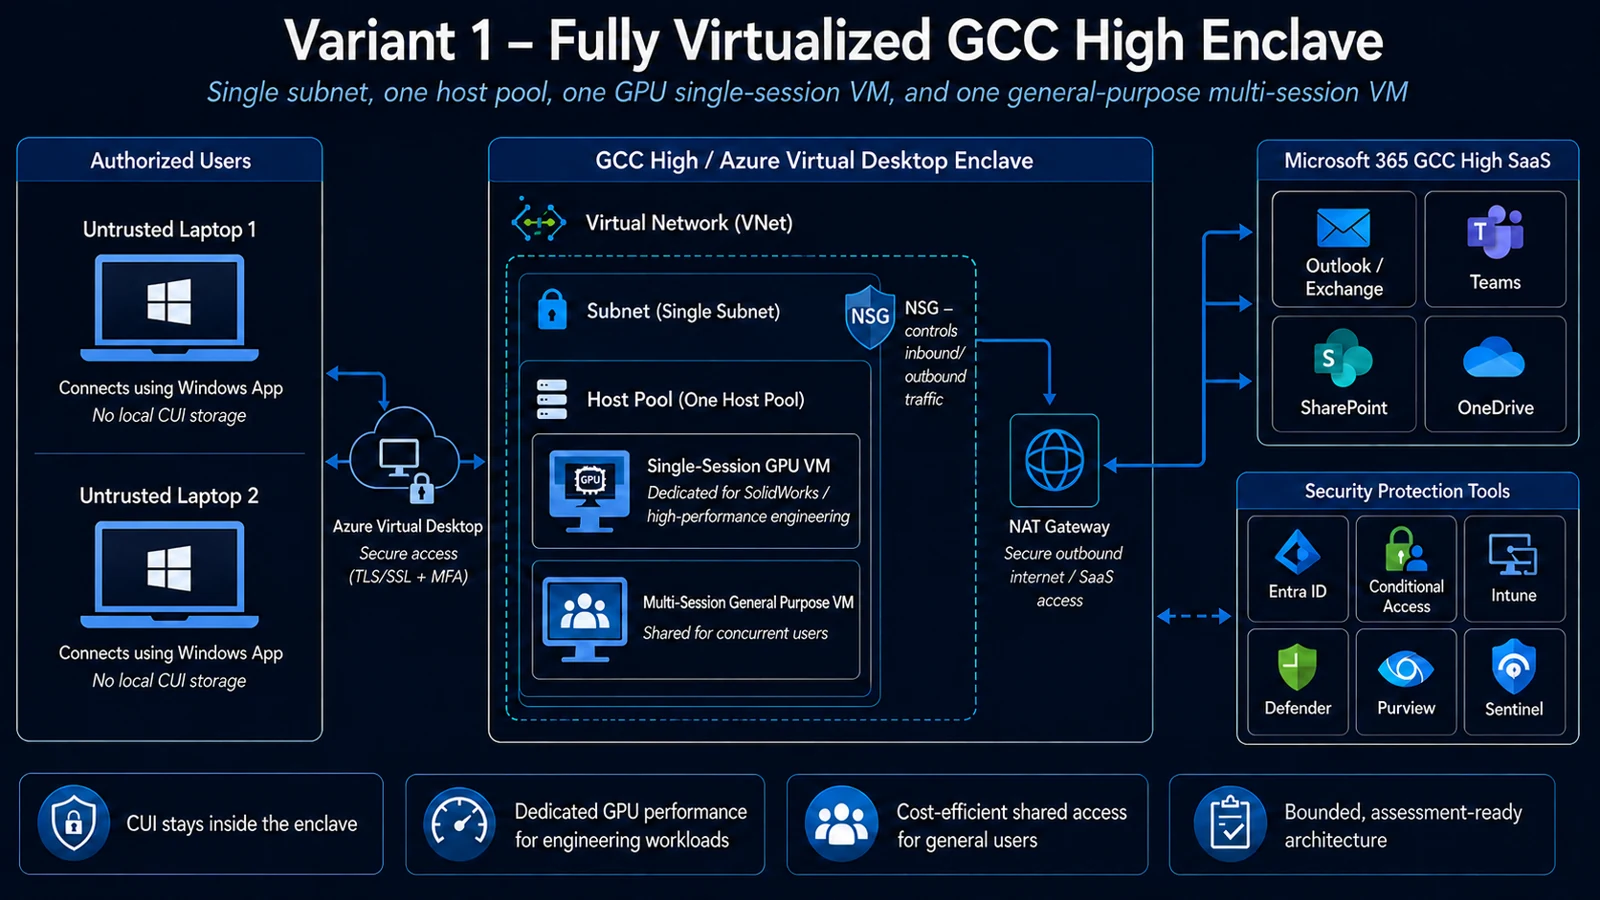
Keep controlled work inside a focused Azure Government virtual desktop and Microsoft 365 GCC High boundary. Users reach their workspace through Windows App; approved applications and information stay in the enclave.

Variant 1 — Fully virtualized enclave reference diagram
Reference illustration. Select the image to send an inquiry or schedule an appointment. Service configuration and control responsibilities are validated for the actual deployment.
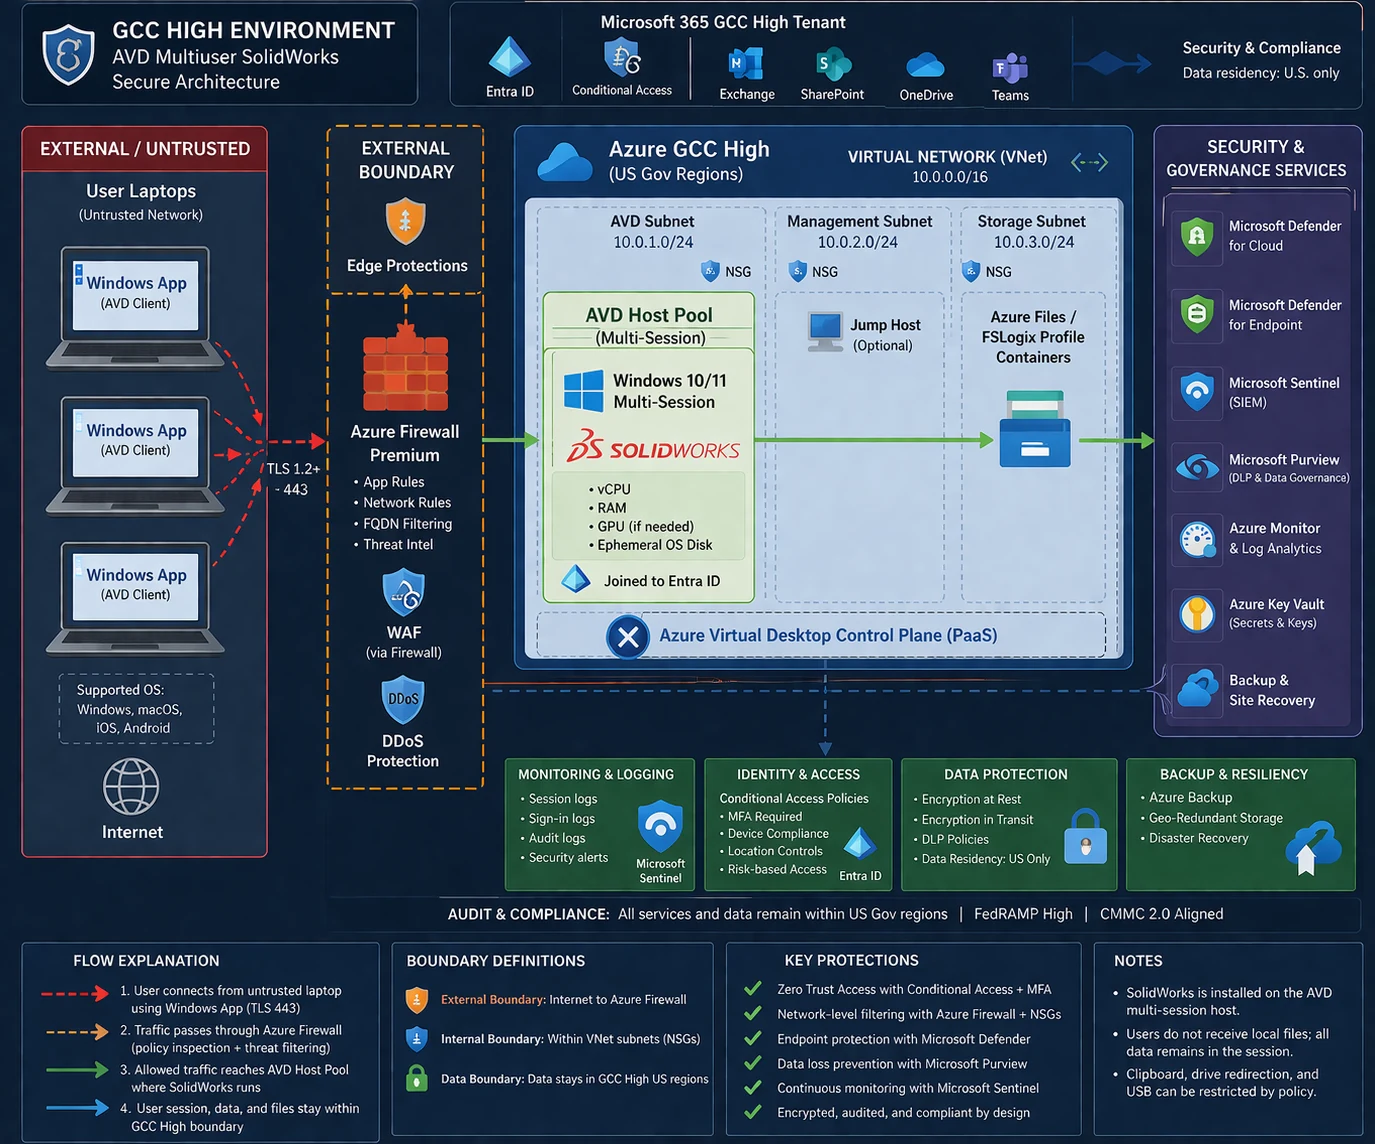
Cloud architecture and data flow
Cloud architecture and data flow. The customer workflow and implemented controls determine the final configuration.

Who this fits

A bounded user population working primarily with email, documents, collaboration, web applications, and Windows engineering software.
What belongs in the boundary

AVD hosts, approved cloud storage and collaboration, identity policies, administration, logging, backup, and the people and processes supporting CUI. Remote access devices and external services must still be classified within the actual scope.

Implementation work

  • Map users, contracts, CUI inputs, applications, and output restrictions.
  • Design general-purpose multi-session capacity, dedicated sessions or GPU workloads where required, and application dependencies.
  • Configure identity, session restrictions, controlled egress, data protection, and approved storage.
  • Test clipboard, drive, print and USB restrictions; exercise monitoring, recovery, and user procedures.

Evidence and operating responsibilities

  • Boundary and data-flow records; asset and authorized-user inventories.
  • Configuration baselines, control narratives, owner assignments and operating procedures.
  • Validation results, access reviews, monitoring records and recovery tests.

Decisions to resolve before deployment

Choose another model if the workflow requires local CUI files, unmanaged peripherals, or direct connections to specialized equipment. A cloud boundary does not remove personnel, physical, or operational responsibilities.